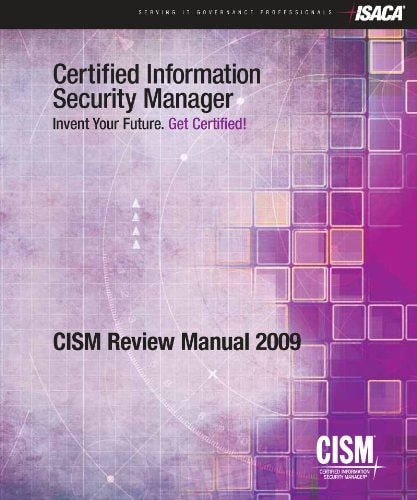
2009 CISM Review Manual
0
0
As an Amazon Associate and affiliate partner, Menrva Books earns from qualifying purchases. Learn more
Author Description
The CISM Review Manual 2009 is a comprehensive reference guide designed to assist individuals in preparing for the Certified Information Security Manager® (CISM®) exam and individuals wishing to understand the roles and responsibilities of an IS manager. The manual has evolved extensively over the past five editions and now represents the most current, comprehensive, globally peer-reviewed information security management resource available. In response to the evolving field of information security management, the extensively expanded and revised 2009 version of the CISM Review Manual continues to move away from the subject of technology and closer to the strategic governance and management aspects of security. There is increasing emphasis on the overarching concepts essential for effective information security management in addition to a focus on the critical thinking and sound judgment required for development and management of increasingly massive and complex security systems and related processes. This publication includes a new and expanded approach to the development of effective security management metrics, based on research projects sponsored by the IT Governance Institute. There is a substantial increase in the scope and depth of coverage on risk management. An expanded focus and structural improvement is included for information security program development as well as a greater concentration on architecture and metrics. The improved approach to management metrics has been carried through to the section on information security management, providing processes to improve overall effectiveness. Also included are case studies to assist the candidate in understanding current practices, definitions of terms most commonly found on the exam, practice questions similar in content to the certification exam and references to additional study materials on specific topics. This manual can be used as a stand-alone document for individual study or as a guide or referen
Menrva's Summary
THE THESIS
This manual serves as a comprehensive guide for the Certified Information Security Manager (CISM) exam and for understanding IS management roles. The 2009 edition emphasizes strategic governance and management over technology, focusing on critical thinking and sound judgment for complex security systems. It incorporates new research on security management metrics from the IT Governance Institute and expands coverage on risk management, information security program development, architecture, and metrics. The manual aims to improve overall security management effectiveness through enhanced processes and provides case studies, exam definitions, practice questions, and study references.
THE SCOPE MAP
- Comprehensive coverage of information security management domains relevant to the CISM exam.
- Expanded focus on strategic governance, risk management, and security program development.
- New and improved approach to developing effective security management metrics.
- Case studies illustrating current information security practices.
- Definitions of key terms commonly found on the CISM certification exam.
- Practice questions designed to mirror the content and style of the certification exam.
- References to additional study materials for in-depth exploration of specific topics.
THE AUTHORITY PERSPECTIVE
The CISM Review Manual 2009 is presented as the most current, comprehensive, and globally peer-reviewed resource for information security management. Its extensive revisions for the 2009 edition reflect a strategic shift towards governance and management aspects, moving away from purely technological subjects. The inclusion of new research on metrics and expanded coverage of risk management and program development are highlighted as key improvements. The manual is designed to equip individuals with the critical thinking and judgment necessary for effective security leadership.
Page Count:
357
Publication Date:
2008-01-01
Publisher:
Information Systems Audit and Control Association
ISBN-10:
1604200375
ISBN-13:
9781604200379
Non-Fiction
Business
IT Management
Information Security
Professional Development
Community Tags
Similar Books




Reader Comments
Share Your Thoughts
No comments yet. Be the first to share your thoughts!