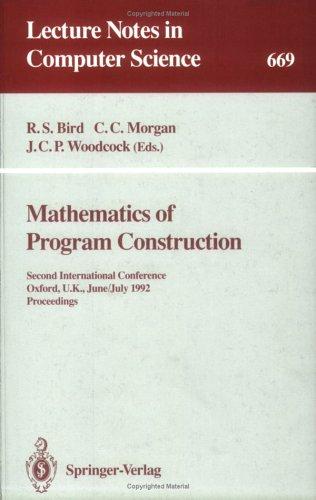
Mathematics of Program Construction
0
0
As an Amazon Associate and affiliate partner, Menrva Books earns from qualifying purchases. Learn more
Author Description
Author description coming soon. We're reaching out to them in the ether...
Menrva's Summary
THE THESIS
This book investigates the application of mathematical reasoning to the construction and verification of computer programs. It explores how formal methods can be used to ensure program correctness and efficiency, moving beyond traditional ad-hoc debugging. The work is grounded in the principles of logic and discrete mathematics, presenting a framework for developing software with provable properties.
THE SCOPE MAP
- Formal methods for program specification and refinement
- Techniques for program correctness proofs
- Algebraic methods for program design
- Case studies demonstrating the application of these techniques
THE AUTHORITY PERSPECTIVE
The book is recognized as a foundational text in the area of program construction using formal methods. Its rigorous approach is often cited by academics and researchers in computer science, particularly those focused on software verification and theoretical computer science. The material suggests a text that is dense and requires a strong background in mathematics and logic, likely appealing to advanced students and professionals in the field.
Page Count:
378
Publication Date:
1993-01-01
ISBN-10:
3540566252
Science & Technology
Science
Non-Fiction
Programming
Logic
Computer Science
Community Tags
Similar Books