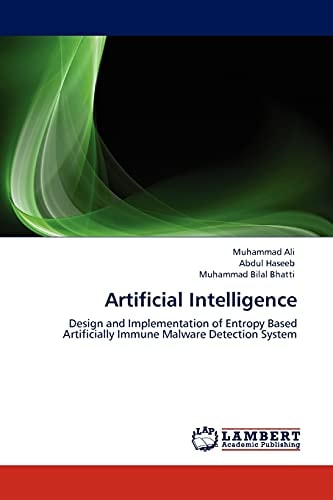
Artificial Intelligence
0
0
As an Amazon Associate and affiliate partner, Menrva Books earns from qualifying purchases. Learn more
Author Description
Many Malware detection systems these days are using signature based techniques to detect malwares and viruses. The zero day or new infected files are not detected by these signature based Anti Viruses and their signature is generated only after they have done their damage. Hence it becomes very important for a user to constantly update the antivirus software. To overcome these problems, we have proposed a solution based on Artificial Intelligence techniques. So the clients will not require frequent updates and probability of detecting zero day infections will rise abruptly. This project is based on implementing data mining algorithms mainly C4.5 Decision Tree learner. We have generated a dataset on the basis of already known malicious executable files. A C4.5 decision tree is generated based on the generated dataset and the unknown executables are passed through the tree to classify the executable as a malicious or a benign file. The purpose is to get rid of the manual signature based Malware detection systems that require constant updated signatures and making systems artificially immune to unknown and zero day malicious executables.
Menrva's Summary
THE THESIS
This book proposes an Artificial Intelligence-based solution to enhance malware detection capabilities beyond traditional signature-based methods. The authors address the limitations of current antivirus software, which often fail to detect zero-day or new infections until after damage has occurred, necessitating frequent updates. Their project implements data mining algorithms, specifically the C4.5 Decision Tree learner, to classify executable files as malicious or benign. By generating a dataset of known malicious files and building a decision tree, the system aims to provide artificial immunity against unknown threats without constant signature updates.
THE SCOPE MAP
- Explanation of the limitations of signature-based malware detection systems.
- Proposal of an Artificial Intelligence-based approach for malware detection.
- Implementation of data mining algorithms, focusing on the C4.5 Decision Tree learner.
- Generation of a dataset based on known malicious executable files.
- Construction of a C4.5 decision tree for classification.
- Methodology for classifying unknown executables as malicious or benign.
- Objective to reduce reliance on manual signature updates for antivirus software.
- Aim to increase the probability of detecting zero-day infections.
THE AUTHORITY PERSPECTIVE
The authors present a technical approach to a persistent cybersecurity challenge, focusing on the practical application of AI and data mining techniques. The proposed solution aims to improve the detection rates of novel malware by leveraging machine learning algorithms, thereby reducing the dependency on frequent manual updates characteristic of traditional antivirus software. The methodology described suggests a systematic process for building and utilizing a decision tree for classification tasks within the cybersecurity domain. This work appears to be a focused study on a specific aspect of malware detection, offering a potential pathway toward more proactive and adaptive security systems.
Page Count:
76
Publication Date:
2011-08-01
Publisher:
Lap Lambert Academic Publishing GmbH KG
ISBN-10:
3845429992
ISBN-13:
9783845429991
Science
Science & Technology
Non-Fiction
Computer Science
Machine Learning
Cybersecurity
Data Mining
Community Tags
Similar Books