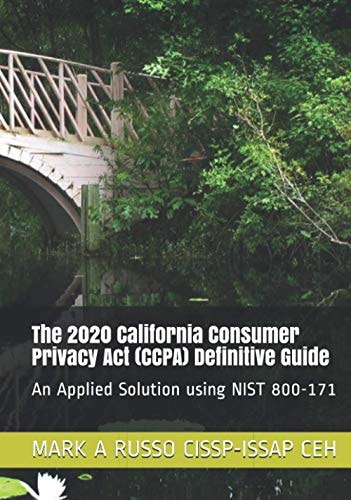
The 2020 California Consumer Privacy Act (CCPA) Definitive Guide: An Applied Solution using NIST 800-171
0
0
As an Amazon Associate and affiliate partner, Menrva Books earns from qualifying purchases. Learn more
Author Description
WELCOME TO THE 2021 RELEASE OF THE OF THE CCPA DEFINITIVE GUIDE. The author has over 25 years in program management, intelligence operations, and cybersecurity and is the #1 expert on NIST 800-171 cybersecurity application of these security controls. In this edition, we have included information and changes affecting businesses attempting to meet the current CCPA deadlines. The author has included an additional chapter on current 2019-2020 amendments, and provides a plain-English interpretation for the reader. Understanding what the CCPA is and how to effectively apply the NIST 800-171 Security Framework is the approach of this how-to guide. The 2020 California Consumer Privacy Act (CCPA) Guide designed to provide clear direction and understanding of how to implement the CCPA either in a business, agency or organization. The CCPA provides provisions specific to California residents and the companies regarding the 2018 compulsory law to protect personal information statewide. While NIST 800-series cybersecurity publications tell a business “what” is required, they do not necessarily help in telling “how” to meet the 110 security control requirements in NIST 800-171. This book is also written to explain what the National Institute of Standards and Technology (NIST) 800-171 security controls require and how to meet them effectively for the purposes of CCPA compliance. And, will walk you and your IT staff through the security controls in enough detail to ensure a complete and "good faith" security effort has occurred. Mr. Russo is the former Chief Information Security Officer (CISO) for the Department of Education where he and his team were responsible for closing over 95% of the outstanding security findings identified by the House Oversight Committee in 2016. He was also a Senior Information Security Engineer with the Department of Defense's (DOD) F-35 Joint Strike Fighter program. He has an extensive background in cybersecurity and is an expert in the Risk Managemen
Menrva's Summary
THE THESIS
This guide provides a practical, step-by-step approach to achieving compliance with the California Consumer Privacy Act (CCPA) by applying the NIST 800-171 cybersecurity framework. The author, Mark A. Russo, leverages over 25 years of experience in program management, intelligence operations, and cybersecurity, positioning himself as a leading expert in the application of NIST 800-171 controls. This edition addresses recent amendments and provides a clear, plain-English interpretation of the CCPA's requirements for businesses, agencies, and organizations. It aims to bridge the gap between understanding
THE SCOPE MAP
- Detailed explanation of the California Consumer Privacy Act (CCPA) provisions.
- Application of the NIST 800-171 Security Framework to CCPA compliance.
- Plain-English interpretation of CCPA amendments from 2019-2020.
- Guidance on meeting the 110 security control requirements of NIST 800-171.
- Strategies for ensuring a complete and "good faith" security effort.
- Insights from the author's experience as former CISO for the Department of Education and Senior Information Security Engineer for the F-35 Joint Strike Fighter program.
THE AUTHORITY PERSPECTIVE
This how-to guide is designed to offer clear direction for businesses, agencies, and organizations seeking to implement the CCPA. It focuses on explaining the National Institute of Standards and Technology (NIST) 800-171 security controls and how to meet them effectively for CCPA compliance. The author's extensive background in cybersecurity, including roles at the Department of Education and the F-35 program, lends significant authority to the practical advice provided. The material suggests a dense, specialist text aimed at IT staff and compliance officers needing actionable steps.
Page Count:
288
Publication Date:
2021-03-19
Publisher:
Independently published
ISBN-13:
9798725069396
Self-help
Non-Fiction
Business
Technology
Law
Community Tags
Similar Books

Reader Comments
Share Your Thoughts
No comments yet. Be the first to share your thoughts!